
Semgrep
SoftwareA fast, developer-friendly static analysis tool that finds security bugs and enforces code standards across your codebase.

About Semgrep
Semgrep is a fast, open-source-rooted static analysis tool that helps developers and security teams find bugs, security vulnerabilities and code-quality issues across their codebases — and enforce their own standards — without the slowness and noise that plague traditional SAST tools. Its name hints at its approach: "semantic grep," a way to search code for patterns based on its structure and meaning, not just text, making it both powerful and approachable for developers.
The key to Semgrep's popularity is that it's genuinely developer-friendly. Writing custom rules is intuitive — they look much like the code you're trying to match — so teams can codify their own best practices, catch specific anti-patterns, and prevent classes of bugs from recurring, all without becoming static-analysis experts. It ships with a large library of community and curated rules covering common security vulnerabilities across many languages and frameworks, so you get value immediately, and it runs fast enough to fit into local development and CI pipelines without grinding things to a halt.
For security teams, Semgrep provides a scalable way to embed security checks directly into the development workflow, catching issues early — when they're cheapest to fix — rather than late in a heavyweight audit. It can scan code, dependencies and secrets, integrate with CI/CD and code hosts, and give teams a clear, low-noise stream of actionable findings. This shift-left, developer-centric philosophy has made Semgrep a favorite among engineering and AppSec teams that want effective security and code governance without alienating developers with slow, false-positive-ridden tools. For organizations that want to find vulnerabilities, enforce standards and improve code quality in a way developers will actually adopt, Semgrep offers a fast, flexible and pragmatic solution that has earned its strong reputation in the security community.
Tags
Ratings & reviews
No ratings yet
Be the first to rate Semgrep — your honest take helps others decide.
- No reviews yet — be the first to rate Semgrep.
Similar softwares
IcyZip
Pair two browsers by QR code to share end-to-end encrypted live text and one selected file.
TempMail.is
Free disposable email. No signup. Persistent inbox for OTPs, signups, and testing.
Ship-Safe Check
Ship-Safe Check - x402 $25 USDC (Solana) gate for AI-built apps + free guides. Returns ship / ship_with_conditions / dont_ship JSON. Not a pentest.
Compare Semgrep
Similar software
OncePad
Share a password once. It fades after one read.
Ship-Safe Check
Ship-Safe Check - x402 $25 USDC (Solana) gate for AI-built apps + free guides. Returns ship / ship_with_conditions / dont_ship JSON. Not a pentest.

Oso
A platform and framework for building application authorization — model and enforce who can do what, easily.

Infisical
An open-source secrets manager for syncing API keys and environment variables across your team and infrastructure securely.

Stytch
A developer-first authentication platform for passwordless login, MFA, and fraud prevention you can build in fast.

Socket
Protects your codebase from supply chain attacks by analyzing open-source dependencies for risky behavior.
Related reads
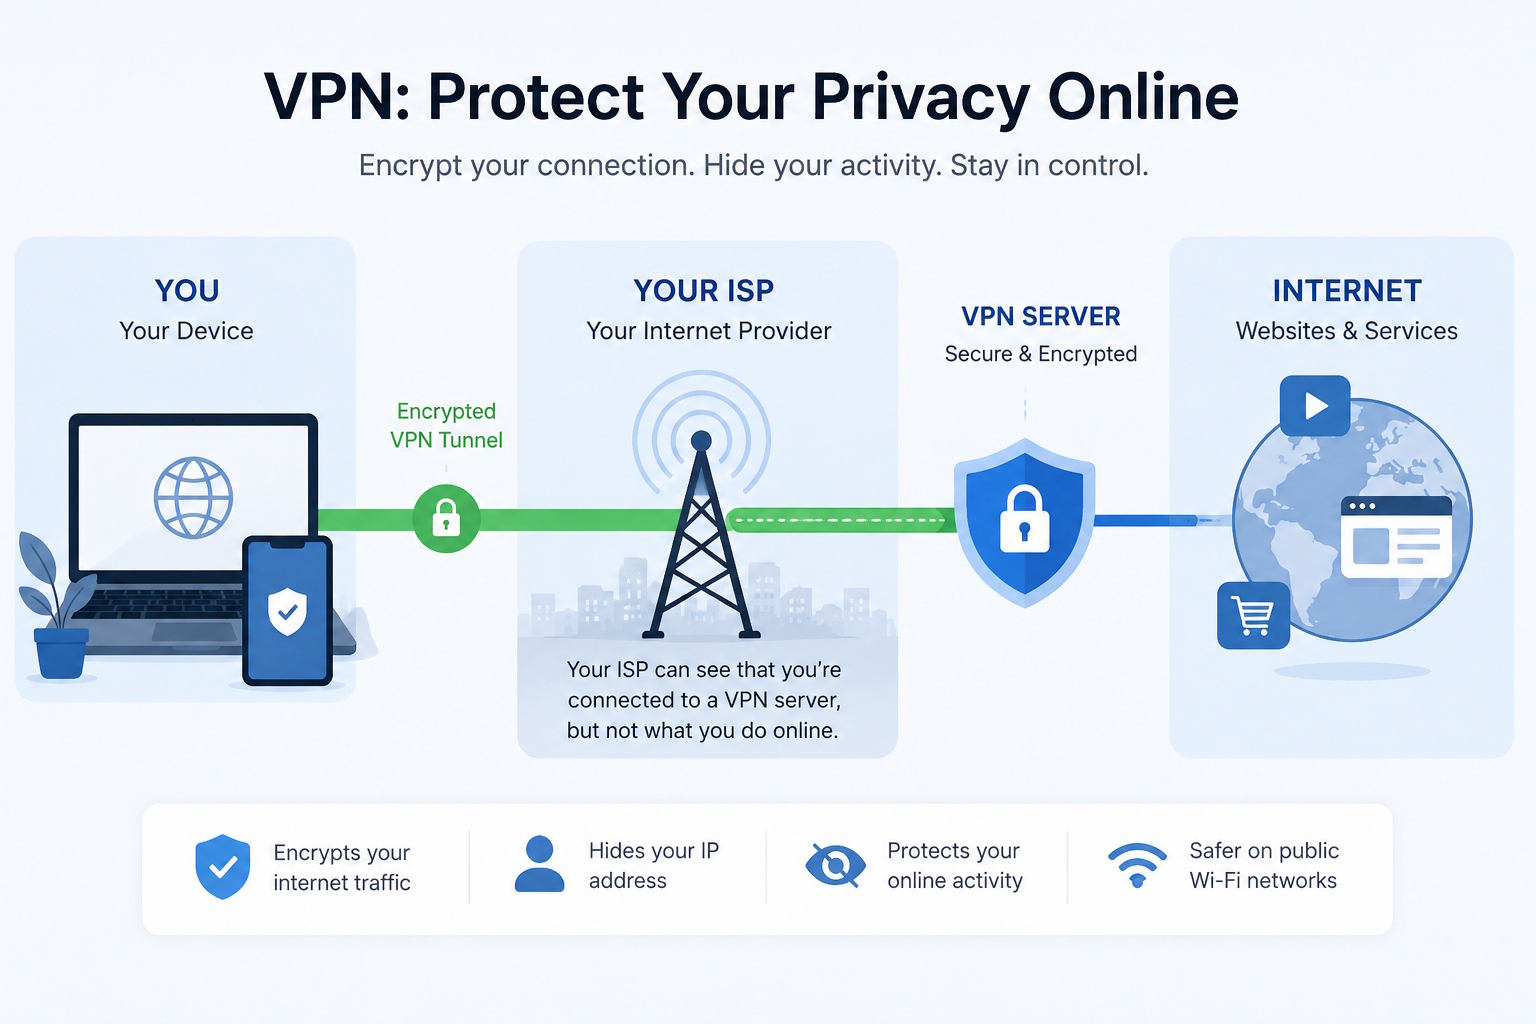
What Can Your ISP See? How a VPN Protects Your Online Privacy
Learn what your ISP can see about your internet activity, what encryption hides, and how a VPN changes the information exposed when you go online.
Craneware Data Breach 2026: What Happened, What Data Was Exposed, and What It Means for Healthcare
Craneware Data Breach 2026
1Password vs LastPass (2026): Which Password Manager Is Safer?
1Password vs LastPass: after LastPass's high-profile breaches, is it still worth it, or should you pay for 1Password? An honest 2026 security-first comparison.
Community discussion (0)
Ask questions, share tips, or compare notes with other Semgrep users.